
Penetration Testing
Network Penetration Testing · Web Application Penetration Testing ·
Cloud Security Testing
Red
TEAM CAPABLE
CVSS
SCORED FINDINGS
100%
REMEDIATION-FOCUSED
Proactive Validation
Our certified ethical hackers follow PTES, OWASP, and industry testing standards to simulate real-world attacks against your network, web applications, and cloud environments — identifying exploitable weaknesses before adversaries do.
Organizations preparing for enterprise customer security reviews, cyber insurance renewals, regulatory audits, or board-level scrutiny benefit most from this proactive validation — moving beyond automated scanning to a defensible, risk-prioritized understanding of true exposure
Services
Validate exposure
before attackers do.
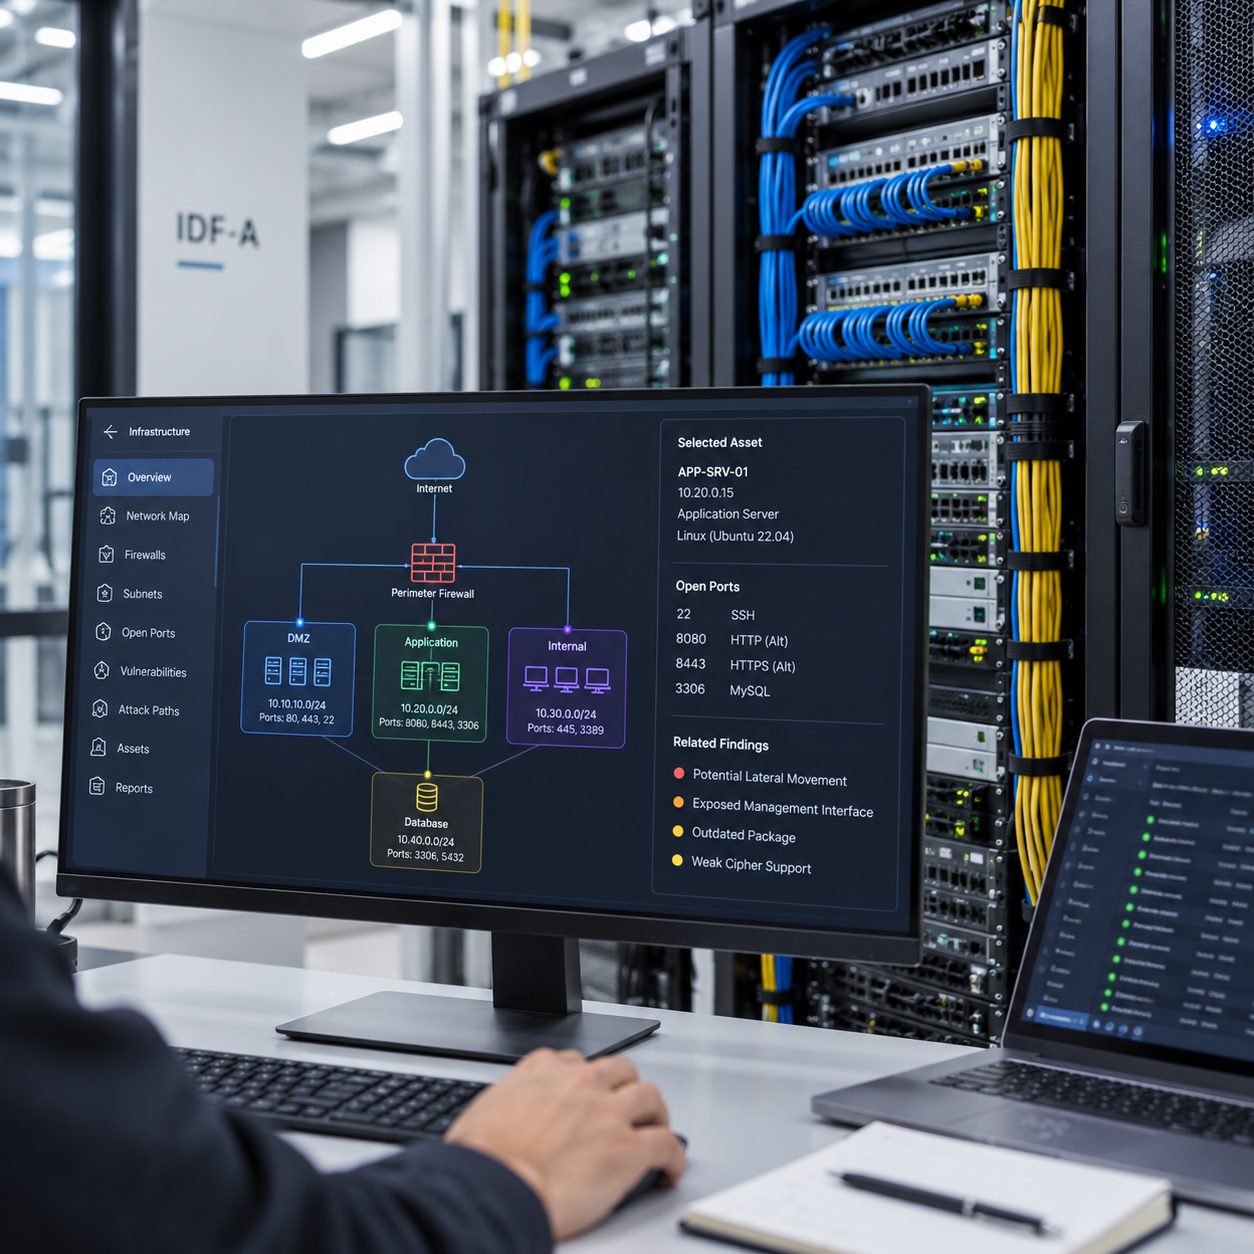
NETWORK PENETRATION TESTING
Network Penetration Testing services are designed for healthcare, medical technology, and regulated organizations that need to validate the real-world security of their internal and external network environments.
This service is ideal for companies preparing for enterprise customer security reviews, cyber insurance renewals, regulatory audits, or board-level scrutiny where documented proof of testing is required. As attackers increasingly target perimeter systems, remote access points, cloud infrastructure, and misconfigured network services, a professional penetration test simulates real-world attack scenarios to identify exploitable weaknesses before malicious actors do.
Organizations that want to move beyond automated scanning and gain a defensible, risk-prioritized understanding of their true exposure benefit most from this proactive security validation.
WEB APPLICATION PENETRATION TESTING
Web Application Security Penetration Testing services are designed for healthcare SaaS platforms, medical technology companies, and regulated organizations that rely on internet-facing applications to deliver services or process sensitive data.
This service is ideal for companies preparing for enterprise customer onboarding, compliance audits, product launches, or investor due diligence where independent validation of application security is required.
Because web applications are a primary target for attackers exploiting vulnerabilities such as authentication flaws, injection attacks, and misconfigurations, a structured penetration test simulates real-world attack techniques to identify exploitable weaknesses before they lead to data exposure or service disruption. Organizations that want to proactively protect patient data, preserve customer trust, and demonstrate security maturity benefit most from this in-depth application security assessment.
CLOUD SECURITY TESTING
Cloud Security Testing services are designed for healthcare, medical technology, and SaaS organizations that rely on AWS, Azure, or other cloud environments to host applications and store sensitive data.
This service is ideal for companies operating in shared-responsibility cloud models where misconfigurations, excessive permissions, exposed storage, and insecure integrations can introduce significant risk. As organizations scale rapidly in the cloud, security controls often lag behind infrastructure growth.
Cloud Security Testing helps identify configuration weaknesses, access control gaps, and exploitable exposure points before they are discovered by attackers, auditors, or enterprise customers. For organizations that must demonstrate secure cloud architecture and defensible security practices, this proactive validation strengthens compliance posture, reduces breach risk, and supports customer trust.
Deliverables
What you receive
from this engagement.
✔ Network Penetration Testing Report
✔ Red-team attack simulation
✔ Exploit chain documentation
✔ Web Application Penetration Testing Results
✔ CVSS-scored findings
✔ Remediation validation retest
Get Started
Build a Security Program
You Can Defend
Schedule an intro call with a seasoned practitioner. We will review your security priorities and map a practical path forward.